Start with the framework decision.
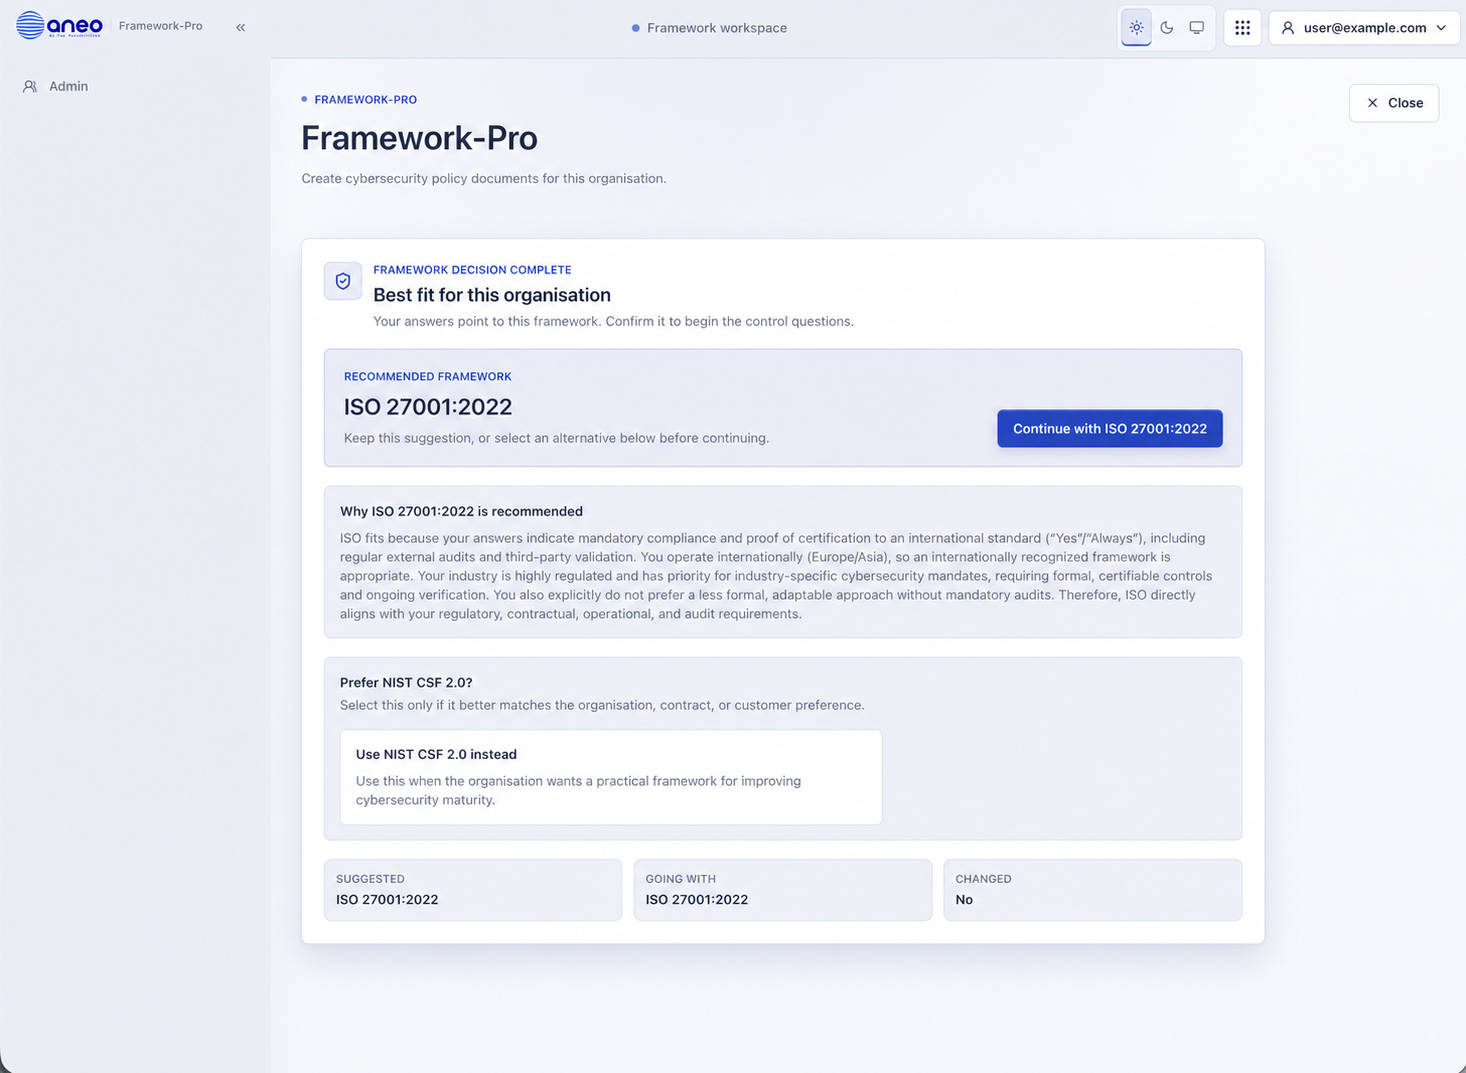
Choose ISO 27001:2022 or NIST CSF 2.0 directly, or answer a short questionnaire for a recommendation. You can continue with the recommendation or choose the other framework; the final choice is recorded.

Framework-Pro helps organizations choose the right security framework, identify applicable controls, and create security policies and supporting documents through a self-service portal.
No certification claims. Clear framework guidance, control mapping, and documentation ready for review.

Framework-Pro is a self-service security framework readiness tool for organizations that need a faster way to choose between ISO 27001:2022 and NIST CSF 2.0, map applicable security controls, and generate tailored, editable security policy drafts and supporting documents from questionnaire answers.
Framework-Pro turns the organisation profile into a framework choice, a focused control set, and editable policy documents with supporting templates.
Choose ISO 27001:2022 or NIST CSF 2.0 directly, or answer a short questionnaire for a recommendation. You can continue with the recommendation or choose the other framework; the final choice is recorded.

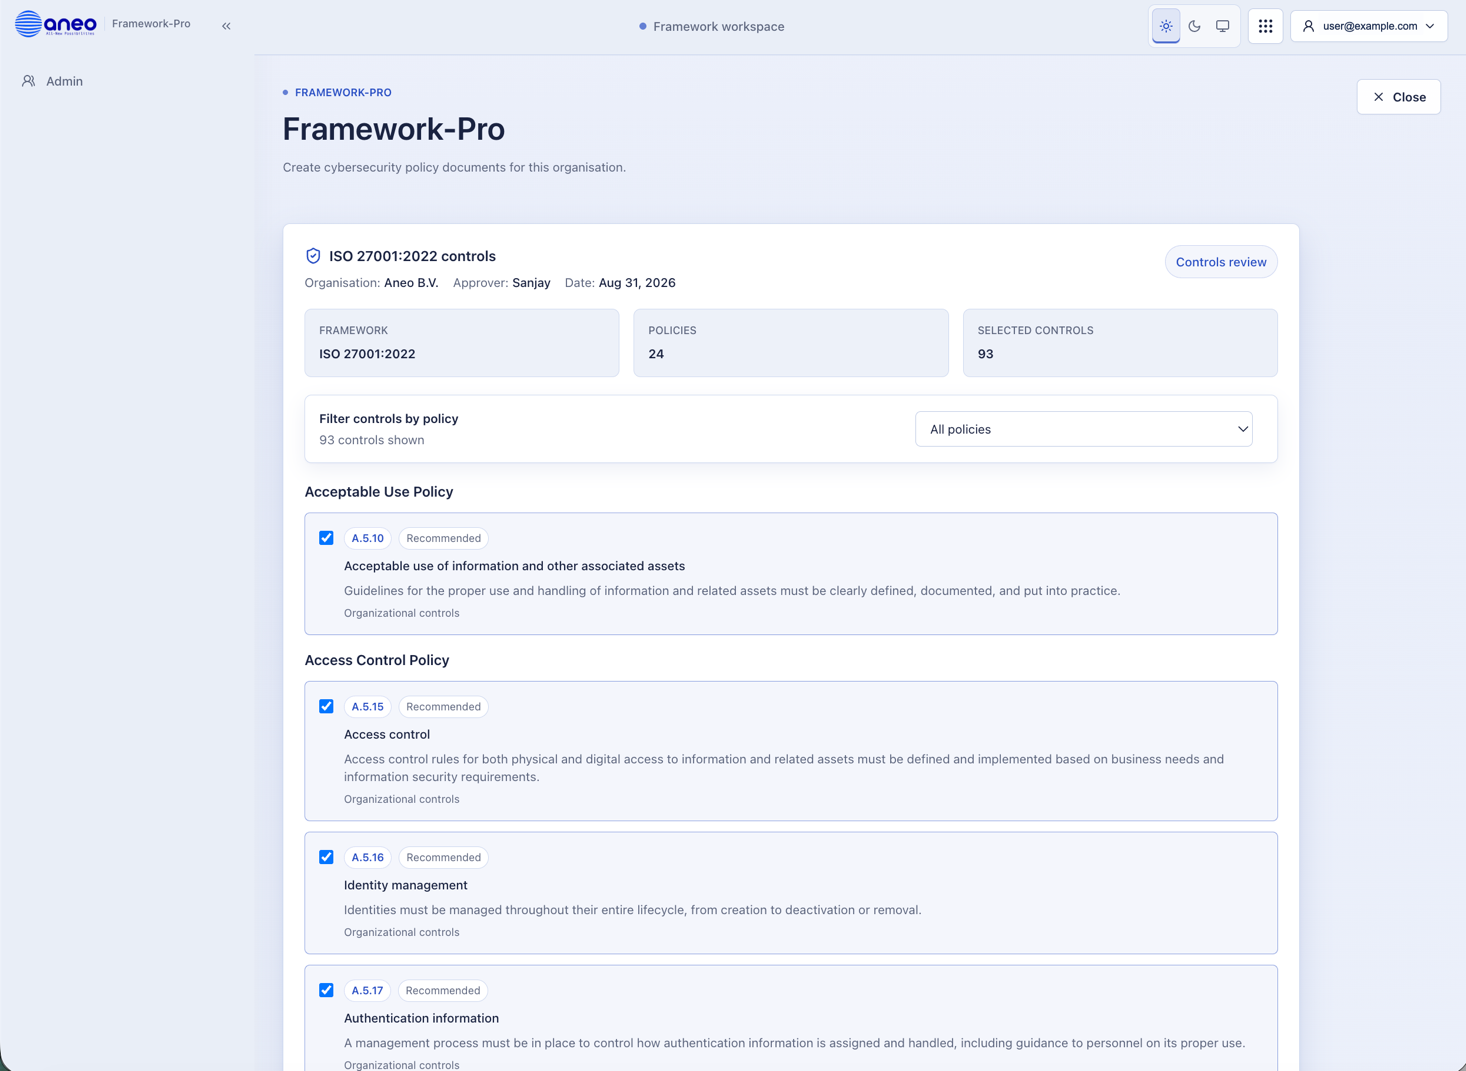
The selected framework determines the control questionnaire and control list. Relevant controls are selected by default, each control includes an explanation, and you can deselect or add controls before submitting.

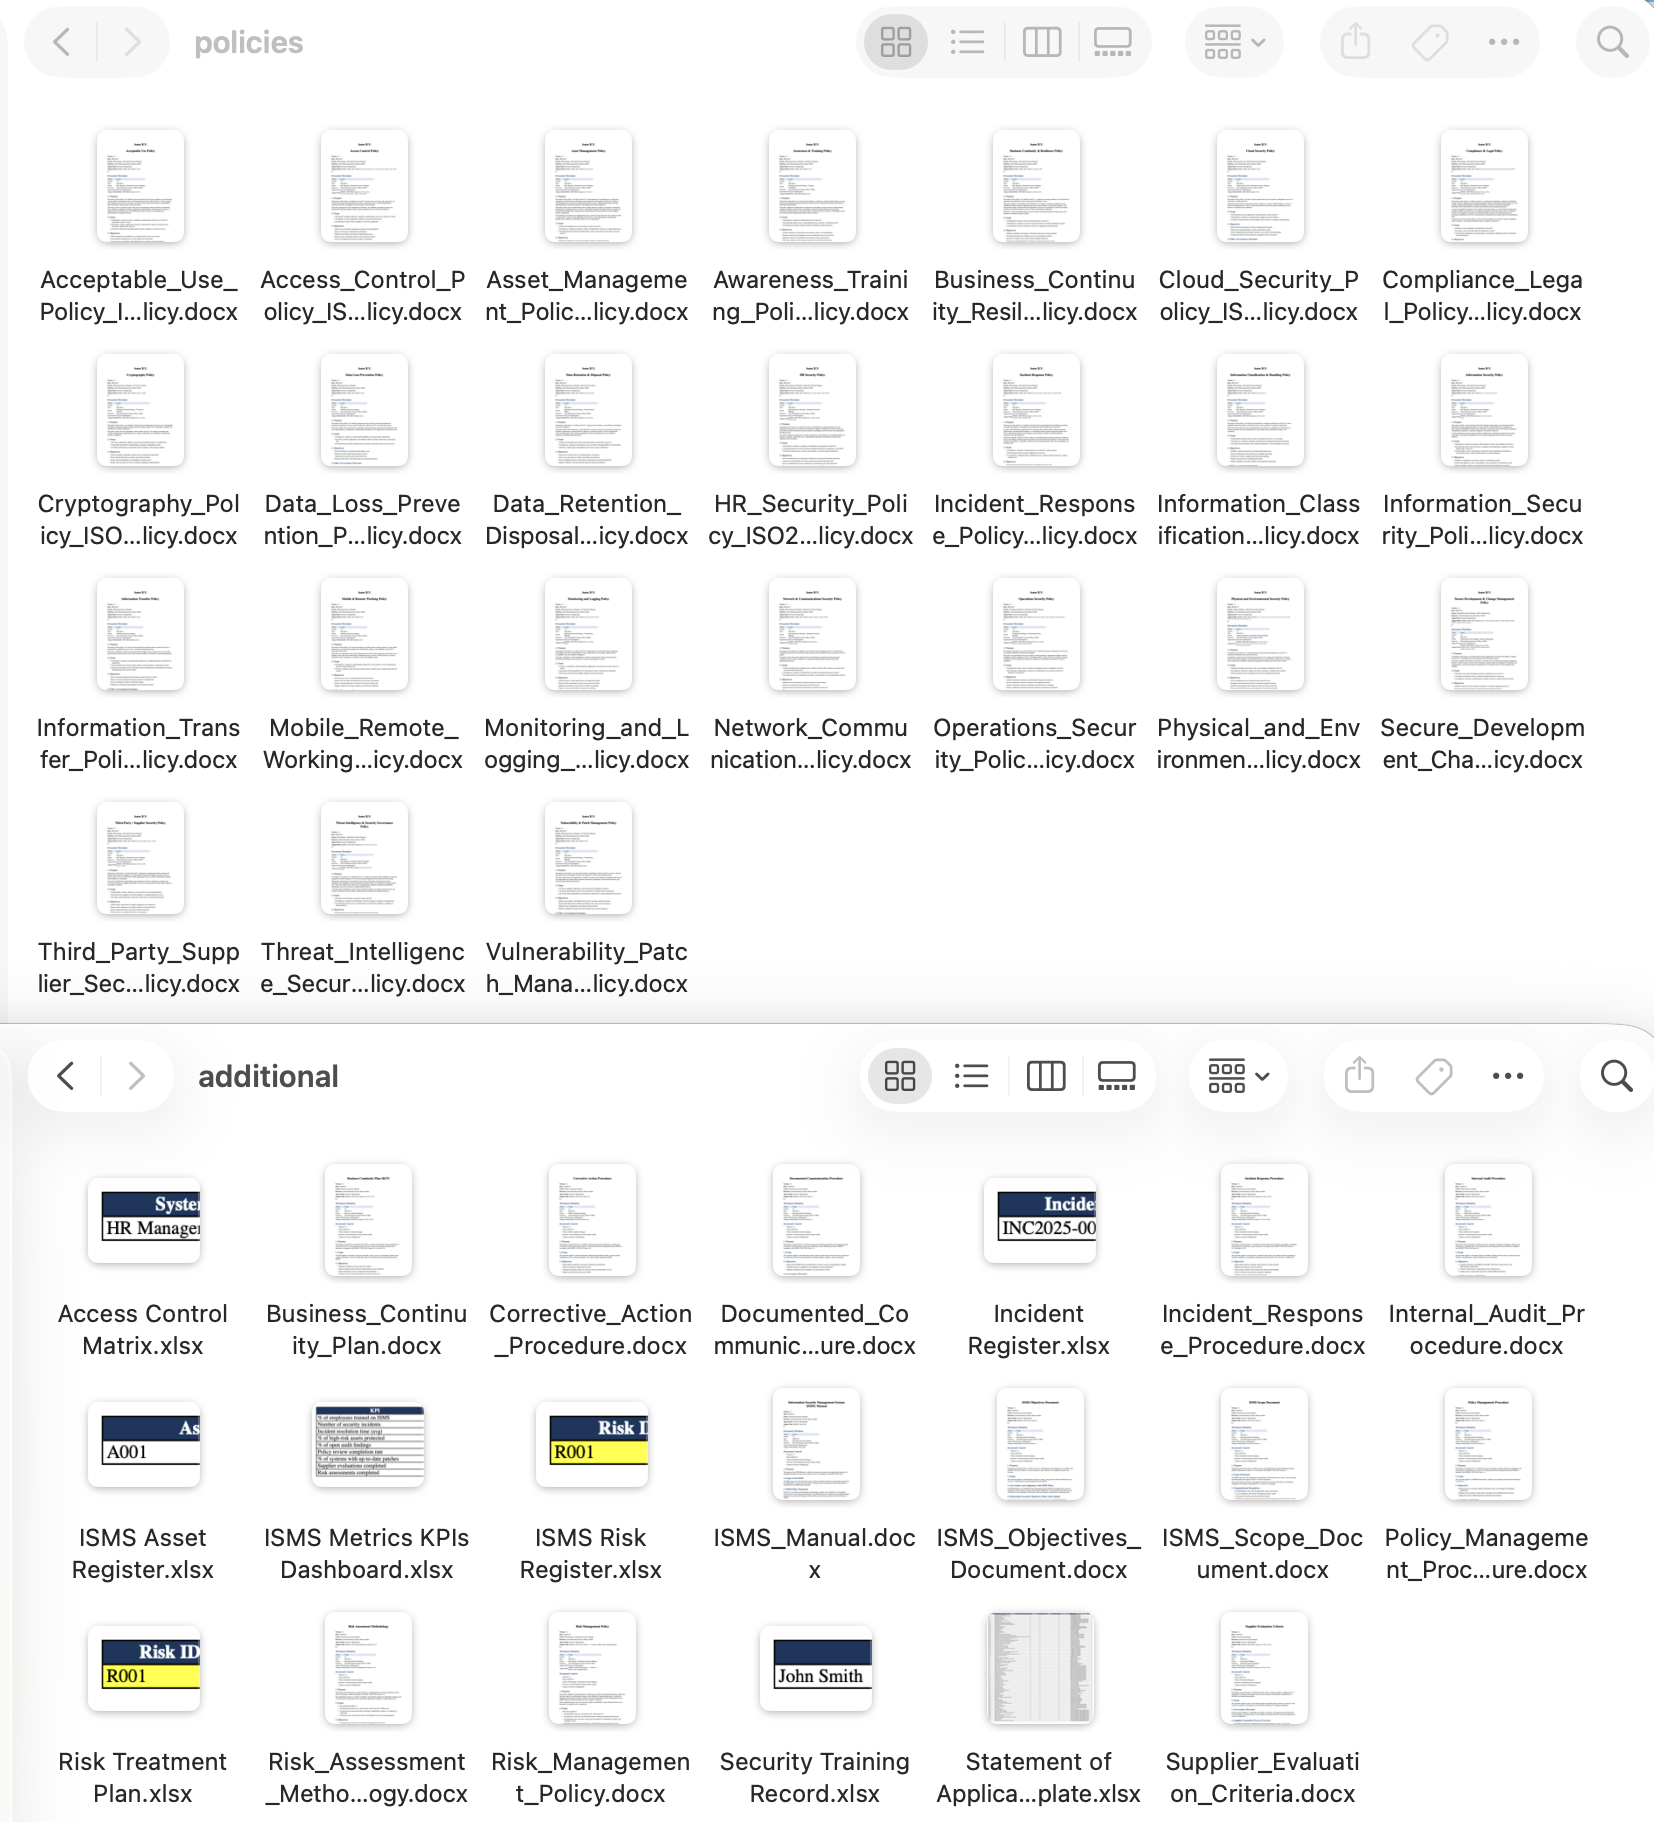
After you submit the selected controls, Framework-Pro generates only the relevant policy documents and includes the complete supporting-document set for the chosen framework in one ZIP download. Supporting documents are standard templates for your team to complete as needed.

Framework-Pro follows a clear sequence: establish the organisation profile, choose the right framework, review the applicable controls, and generate a tailored package your team can review and edit.
Organisation name, executive approver, document date, and the context behind the readiness work.
Choose ISO 27001:2022 or NIST CSF 2.0, with a plain-language recommendation when needed.
Review framework-specific questions, default selections, and explanations before submitting.
Selected controls drive the policy drafts, while supporting documents arrive in the same ZIP.
Framework-Pro is built for teams that need practical readiness output, not another spreadsheet of controls with unclear owners.
Understand whether ISO 27001:2022 or NIST CSF 2.0 is the better first move for your organization.
Reduce control noise by focusing on the security controls that actually apply to your situation.
Generate security policies and supporting documents faster than starting from blank templates.
Organize owners, implementation tasks, and evidence placeholders before customer or audit pressure arrives.
The workflow starts with the organisation profile and ends with documentation your team can review, edit, approve, and use as a readiness baseline.
Enter the organisation name, executive approver, document date, and practical business context that shapes the readiness path.
Select ISO 27001:2022 or NIST CSF 2.0 directly, or answer short questions for a recommendation. Continue with it or override it; the final choice is recorded.
Answer the framework-specific control questions. Relevant controls are selected by default with explanations, and you can add or remove controls before submitting.
Framework-Pro creates only the policy documents tied to selected controls and includes the supporting documents in one ZIP for review and editing.
Framework-Pro helps turn framework selection into a clear decision based on customer expectations, certification needs, security maturity, risk appetite, and operating reality.
Best when customers, partners, or leadership expect a formal information security management system and a certifiable framework path.
Best when the team needs a flexible cybersecurity framework for governance, risk visibility, security operations, and continuous improvement.
The generated output is designed to help teams move from scattered notes to a structured readiness pack. Use it for internal review, customer security conversations, consultant handoff, and audit planning.
Framework-Pro generates structured cybersecurity documentation and control guidance for internal business use. The outputs should be reviewed, approved, implemented, and maintained by your organization. Certification still requires implemented controls and, where applicable, an accredited auditor.
Each explanation focuses on a distinct business or framework need. The questionnaire-based product workflow remains the same.
Generate customised security policy drafts for a small business from questionnaire answers, business context, risks, and selected controls.
Explore this use caseGenerate tailored ISO/IEC 27001:2022 policy drafts and supporting readiness documents from business context and applicable control decisions.
Explore this use caseGenerate tailored NIST CSF 2.0 policy drafts and supporting readiness documents from questionnaire answers and business context.
Explore this use casePrepare tailored security policy drafts and supporting readiness documents when a customer or vendor review asks for security policies.
Explore this use caseFramework-Pro is a self-service security framework readiness tool that helps organizations choose ISO 27001:2022 or NIST CSF 2.0, identify applicable controls, and generate tailored security policy drafts and supporting documents from questionnaire answers.
No. Framework-Pro is not a generic template library. It uses questionnaire answers and selected controls to generate customised policy drafts and supporting readiness documents that teams can review and adapt.
Yes. Framework-Pro uses answers about the organization, data, risk profile, industry, resources, security obligations, framework choice, and applicable controls to tailor the generated policy drafts.
No. Framework-Pro accelerates readiness, documentation, control mapping, and evidence organization. The organization still needs to implement controls and work with an accredited auditor for certification.
No. Framework-Pro provides security readiness guidance and editable documentation drafts for internal business use. It does not provide legal advice and does not replace legal, compliance, auditor, or security professional review.
Yes. Framework-Pro is self-service. Users can create an account in the aneo portal, generate documents, and pay online through the payment gateway.
Framework-Pro supports ISO 27001:2022 and NIST CSF 2.0 for framework selection, control mapping, policy generation, and readiness planning.
Yes. The generated policies and supporting documents are drafts for review. Teams can edit them before internal approval, implementation, customer sharing, or auditor review.
Framework-Pro uses submitted questionnaire answers to generate readiness outputs for the user. Teams should avoid submitting unnecessary sensitive data and should review the generated documents before approval, implementation, or sharing.

Create an account, choose ISO 27001:2022 or NIST CSF 2.0, generate security policies and supporting documents, and pay online through Framework-Pro.
Context in, reviewable documents out.